With the holiday shopping season approaching, retailers are entering one of their most critical periods for both cybersecurity and business continuity. Threats are high, pressure to remediate vulnerabilities is mounting, and the consequences of a disruption during peak shopping can be significant.
But as retailers turn to automation and autonomy to speed up endpoint security, there’s a risk in taking humans out of the equation. A patch may close a security gap while disrupting point-of-sale systems, inventory applications or other technology retailers depend on to keep stores and fulfillment operations running.
The fastest remediation isn’t always the safest decision, especially when a mistake could affect sales during the busiest shopping weeks of the year. Retailers need the speed and scale of automation, but human judgment remains essential when security decisions could disrupt business-critical operations.
Interruption to operations
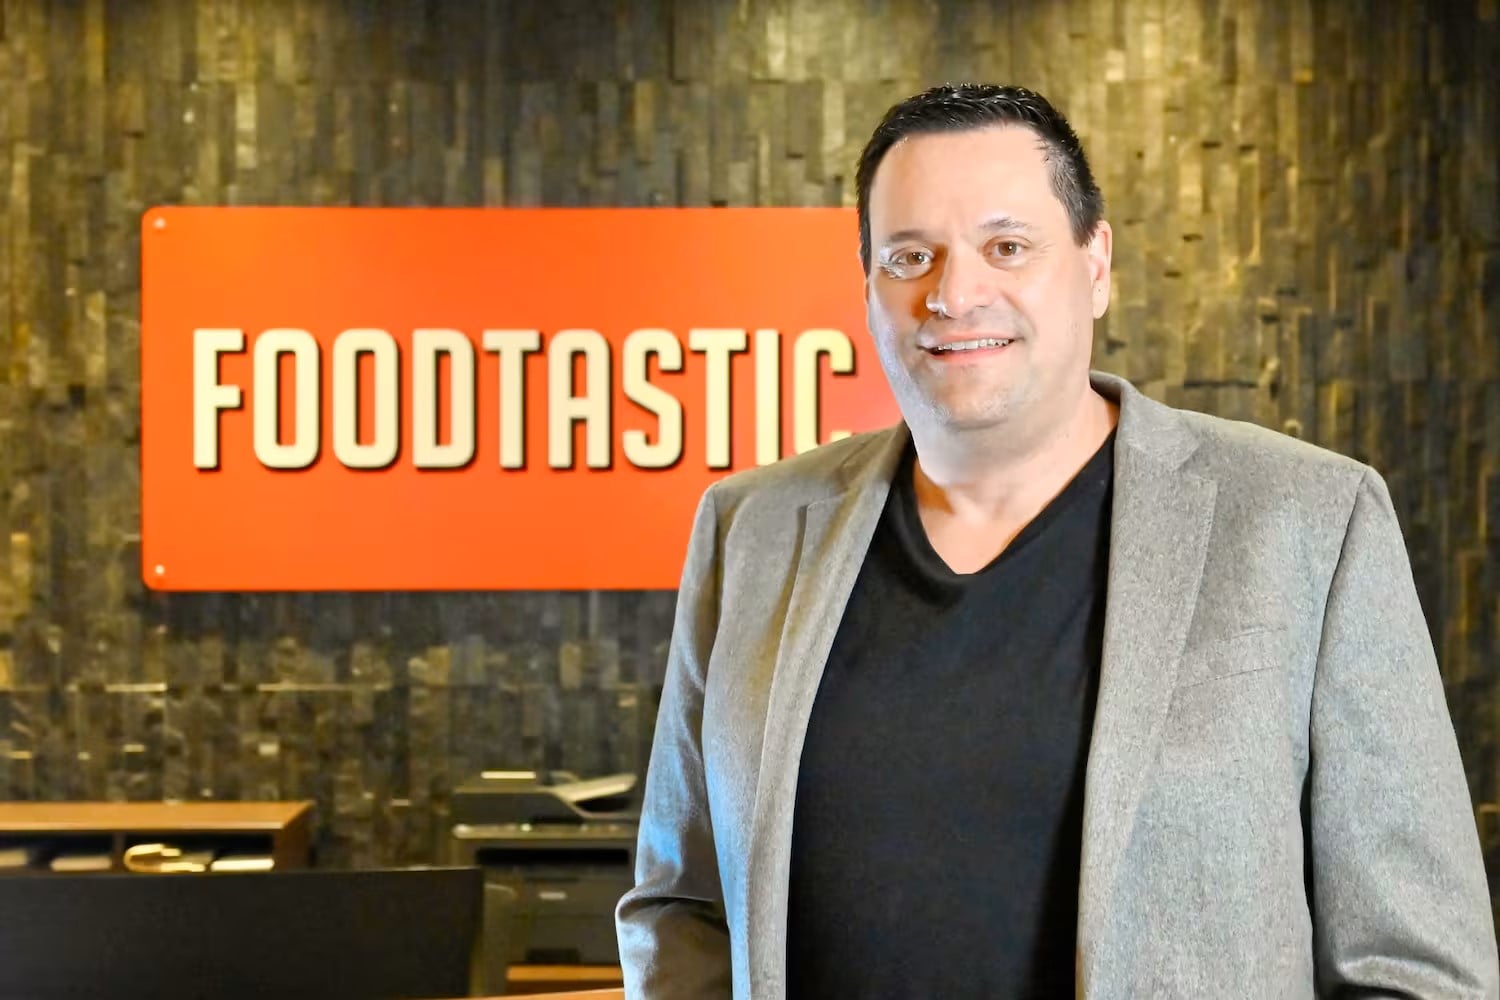
David Sowder, Senior Solutions Architect at Adaptiva, said that during the holiday shopping season, one of the biggest cybersecurity threats retailers face is an interruption to their operations.
“Ransomware and other cyberattacks can bring down point-of-sale systems, disrupt inventory management, or prevent orders from being fulfilled, all at a time when retailers can least afford downtime,” he said.
“While data breaches remain a serious concern, an outage during peak shopping periods can have an even more immediate financial impact. If a customer can’t complete a purchase because a retailer’s systems are down, they’re unlikely to wait around for the issue to be resolved. They’ll simply take their business elsewhere. For retailers, that means a cybersecurity incident can quickly turn into lost revenue and potentially lost customer loyalty.”
Operational risks for retailers
Even a security update intended to protect a retailer can create operational problems if it isn’t properly tested before deployment. A patch could disrupt a point-of-sale application, interfere with inventory systems or change how software functions for employees processing transactions and fulfilling orders, said Sowder.
“During the holiday rush, even a small change to a familiar workflow can create delays that affect customers and sales. That’s why I strongly recommend retailers establish a model store or test environment that mirrors their actual retail operations,” he said.
“Before deploying patches across hundreds of locations, retailers should ensure updates are validated in that environment so critical systems continue functioning as expected. Once those updates have been tested, they can move through progressively larger deployment groups before reaching the broader retail network. This approach helps retailers maintain security while minimizing the risk of disruptions to their busiest operations.”
Determining security cybersecurity vulnerabilities
Retailers should start by prioritizing vulnerabilities that are already being actively exploited, particularly those listed in CISA’s Known Exploited Vulnerabilities catalog. From there, they should evaluate the criticality of other vulnerabilities and focus their resources on the patches that address the greatest security risks, explained Sowder.
“The challenge is that identifying vulnerabilities, determining which patches are needed and deciding what to deploy first can become a significant manual workload. With autonomous patch management, IT teams establish their security policies and operational requirements, while the platform evaluates vulnerabilities, prioritizes remediation and executes the appropriate actions within those guardrails,” he said.
“Even high-priority security patches should be validated in a test environment before reaching production systems. The goal is to accelerate the entire process, from identifying a critical vulnerability to testing and deploying its patch, without skipping the safeguards that keep retail operations running.”
Human oversight and decision-making in cybersecurity
A human-in-the-loop approach starts with IT teams defining security policies, approval requirements and operational constraints, then allowing autonomous systems to execute within those boundaries. The system can evaluate endpoint conditions, prioritize vulnerabilities, prepare and deploy patches, and take additional permitted actions when remediation hasn’t achieved the desired result, said Sowder.
“Human oversight becomes important when an approval is needed before patches reach live retail locations or when something goes wrong during deployment. For example, if an update unexpectedly disrupts a store application, IT teams need the ability to quickly pause deployment, contain the issue or initiate a rollback,” he said.
“This is especially important during the holiday season, when even a brief disruption can affect a large volume of transactions. The key is ensuring those human-directed interventions can be executed just as quickly as the autonomous patching process, so IT teams can maintain control without unnecessarily delaying remediation.”
Practical steps for retailers
Sowder said one of the biggest mistakes retailers can make during the holiday season is implementing a blanket freeze on security updates to avoid disrupting operations. The reasoning behind that approach is sound, but attackers won’t stop exploiting vulnerabilities just because it’s a retailer’s busiest time of year.
“A better strategy is to continue prioritizing and deploying patches for critical or actively exploited vulnerabilities while deferring lower-priority updates when appropriate. Autonomous patch management can help retailers accelerate the entire remediation process, including prioritization, preparation and deployment, while maintaining the safeguards needed to protect critical operations,” he noted.
“Looking ahead to 2027, the time between vulnerability discovery and exploitation continues to shrink, leaving organizations with less time to respond. Retailers need to shorten their patching cycles accordingly, ensuring they can address emerging threats quickly without compromising the systems their businesses depend on.”
More from Retail Insider: